Blog

58 Results / Page 1 of 7

Background
Pen testing and PCI

todaySeptember 10, 2026

close

Blog Jonathan Kimmitt

What to Know About Penetration Testing for PCI

What to Know About Penetration Testing for PCI Organizations that accept, process, store, or transmit payment card information are required to ensure that appropriate security controls are in place to protect the cardholder data environment (CDE). Penetration testing is a major part of validating that those controls are working as ...

Third Party Risk Trojan Horse

todayJune 18, 2026

close

Blog Will Arnett

Third-Party Risk Is Your Biggest Blind Spot

Supply Chain Attacks Explained for Engineers, CISOs, and the “Why Is This My Problem?” Executive Team If cybersecurity had a greatest-hits album, “trusted relationships abused” would be the platinum single on repeat. Firewalls? Hardened.Endpoints? Covered (mostly).Users? Trained (occasionally awake during it). And then… inevitably… someone gets breached through a vendor ...

Live Auction of data from smartphone

todayJune 8, 2026

close

Blog Will Arnett

Smartphone Surveillance Explained: When You’re Probably Not Hacked… But Being Tracked

The Cybersecurity Reality Behind Smartphone Surveillance By design, cybersecurity discussions often begin with intrusion: malware, exploits, nation-state operators lurking in the shadows. But what if the real threat isn’t hiding in your system…because it was never “outside” to begin with? The Myth of the Hack In cybersecurity, language matters. Many ...

Threat Actor Strategies image

todayMay 28, 2026

close

Blog Andrew Hickman

Changing Threat Actor Strategies in 2026 and the Critical Role of Experienced Security Operations

As we move deeper into 2026, cyber threat actors continue to evolve at a pace that challenges even mature security programs. The developments seen throughout 2025—faster attack execution, identity-based intrusions, and widespread use of artificial intelligence—have not slowed. Instead, they have matured into highly efficient, scalable attack models defined by ...

Why passwords are failing us

todayMay 6, 2026

close

Blog Jonathan Kimmitt

Why Passwords Are Failing Us: The Structural Weaknesses of Authentication

Passwords remain the most common authentication method across organizations of every size. However, they also represent one of the most persistent points of failure in modern security programs. Despite decades of policy refinement, user training, and technical controls, password-based authentication routinely enables breaches, account compromise, and lateral movement. This reality ...

Why legal and HR must be involved early in incident response

todayApril 30, 2026

close

Blog Jonathan Kimmitt

Why Legal and HR Must Be Involved Early in Incident Response

Involving legal and HR in incident response is part of running the process correctly. It should never function as an optional or secondary step. Incident response is a business process, not merely a technical one. While security teams focus on containment, investigation, and recovery, legal and HR address obligations, employee ...

Ransomware kill chains are collapsing

todayApril 16, 2026

close

Blog Will Arnett

Ransomware Kill Chains Are Now Measured in Hours… Not Days

What Security Leaders Must Do Next Ransomware is no longer a slow‑burn, multi‑week operation. In April 2026, threat intelligence confirms that modern ransomware campaigns routinely progress from initial access to data encryption in hours, sometimes within a single business day. Attackers are exploiting freshly disclosed vulnerabilities before patches are widely ...

Critical-infrastructure-war

todayApril 7, 2026

close

Blog Will Arnett

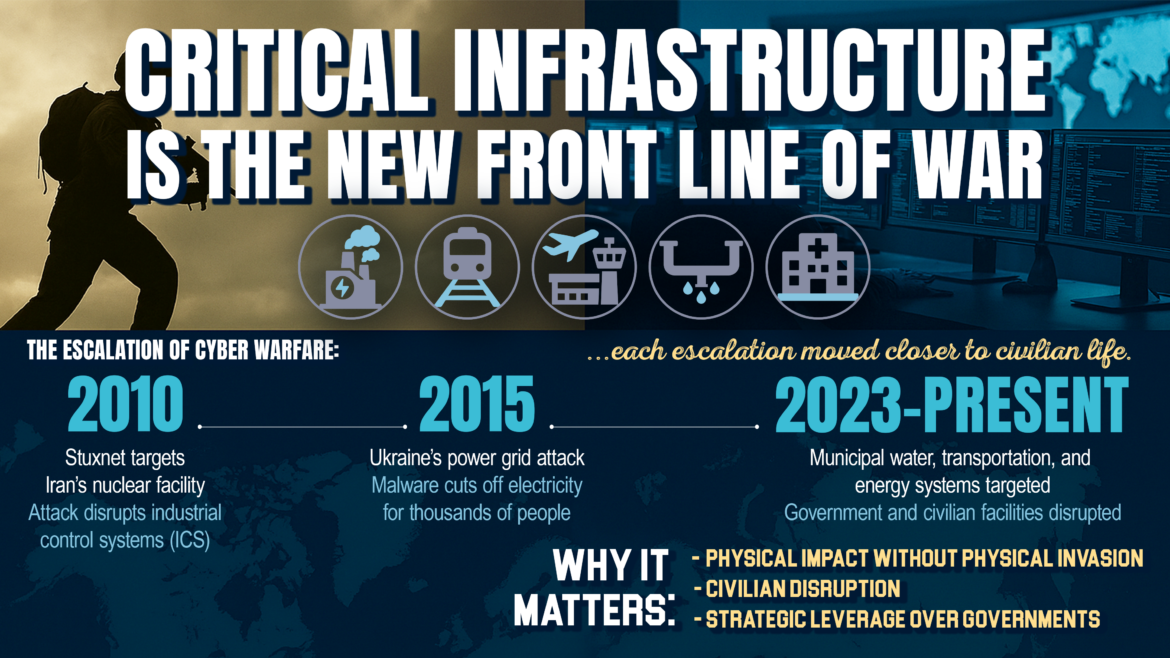
Critical Infrastructure Cyber Attacks and the Changing Face of War

Modern geopolitical conflict has increasingly expanded beyond traditional battlefields – with cyber operations becoming a critical complement to conventional military force. From Kinetic Battlefields to Digital Front Lines Modern conflict is no longer confined to physical terrain. Over the last decade, cyber operations targeting critical infrastructure have moved from a theoretical risk to ...